Chinmay Bhat

Product developer in Bangalore with 3+ years of full-time experience. I build websites that bring in businessproducts for a regulated fintechfintechs ready for PCI and RBI auditsSEO that compoundssecurity for a fleet of Macswebsites that bring in business

Download resume
Works with
Chinmay Bhat

Currently, 3+ years full-time

Product developer at EximPe

100×

organic traffic

Next.jsReactTypeScriptTailwind CSSPostgreSQLPrismaSupabaseTerraformDockerSwiftGoogle Chrome
LaravelWordPressGhostGitHub ActionsGoogle AdsMetaMakeClaudeFigmaGSAPVercel
3+
years of full-time experience
2,640
GitHub contributions since January 2025
100×
organic traffic growth at EximPe
500+
qualified leads from forms I built

One person across design, code, growth and security. Every project is quoted to its scope: pick one and I’ll send a proposal.

Websites that convert

Design and build in Next.js, fast by default, with forms and tracking wired in from day one.

  • A custom design, not a template
  • Built in Next.js: fast, accessible, SEO-ready
  • Lead forms, analytics and conversion tracking
  • A blog or CMS your team can edit
  • Domain, hosting and launch handled for you
  • Next.js
  • Design
  • CMS

SEO and growth

Content, landing pages and free tools that rank, plus Google and Meta campaigns.

  • Technical SEO audit and fixes
  • Content and landing pages that rank
  • Google and Meta ad campaigns
  • Conversion tracking you can trust
  • SEO
  • Ads
  • Analytics

Fintech audits and compliance

Internal ISO 27001 audits, readiness for PCI DSS and RBI audits, and the software that keeps a fintech audit-ready all year.

  • Internal ISO 27001 audits
  • PCI DSS and RBI audit readiness
  • Policies, evidence and access reviews
  • Compliance tooling set up for your team
  • PCI DSS
  • RBI
  • ISO 27001

Internal tools and automation

The dashboards, approval flows and AI assistants your team is paying three SaaS tools for.

  • Dashboards and approval workflows
  • Automations with Make.com and webhooks
  • AI assistants and MCP integrations
  • Deployed on your own AWS or Vercel
  • Automation
  • MCP
  • Claude

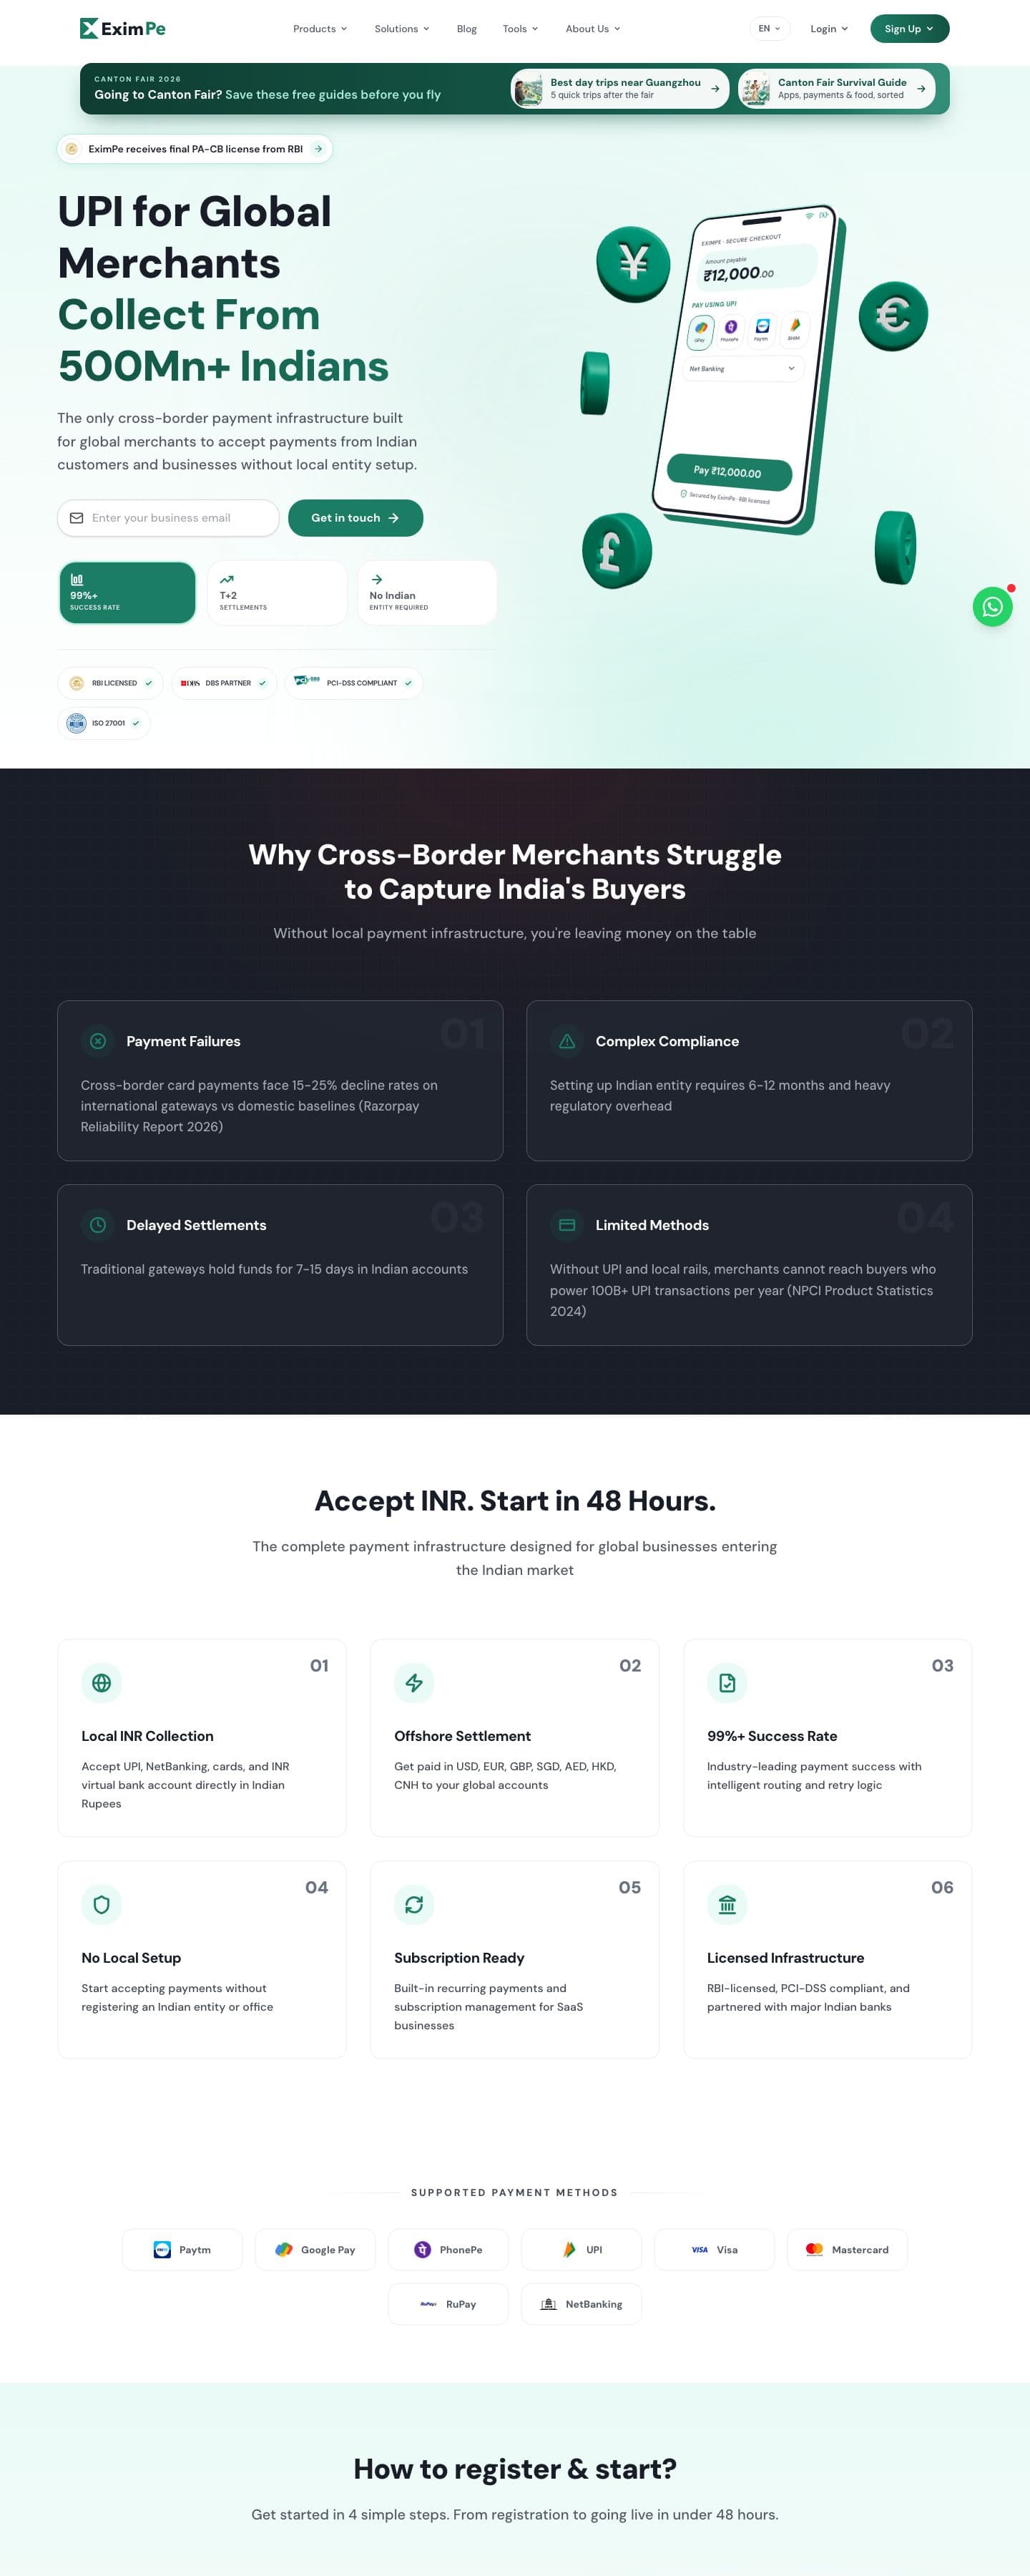
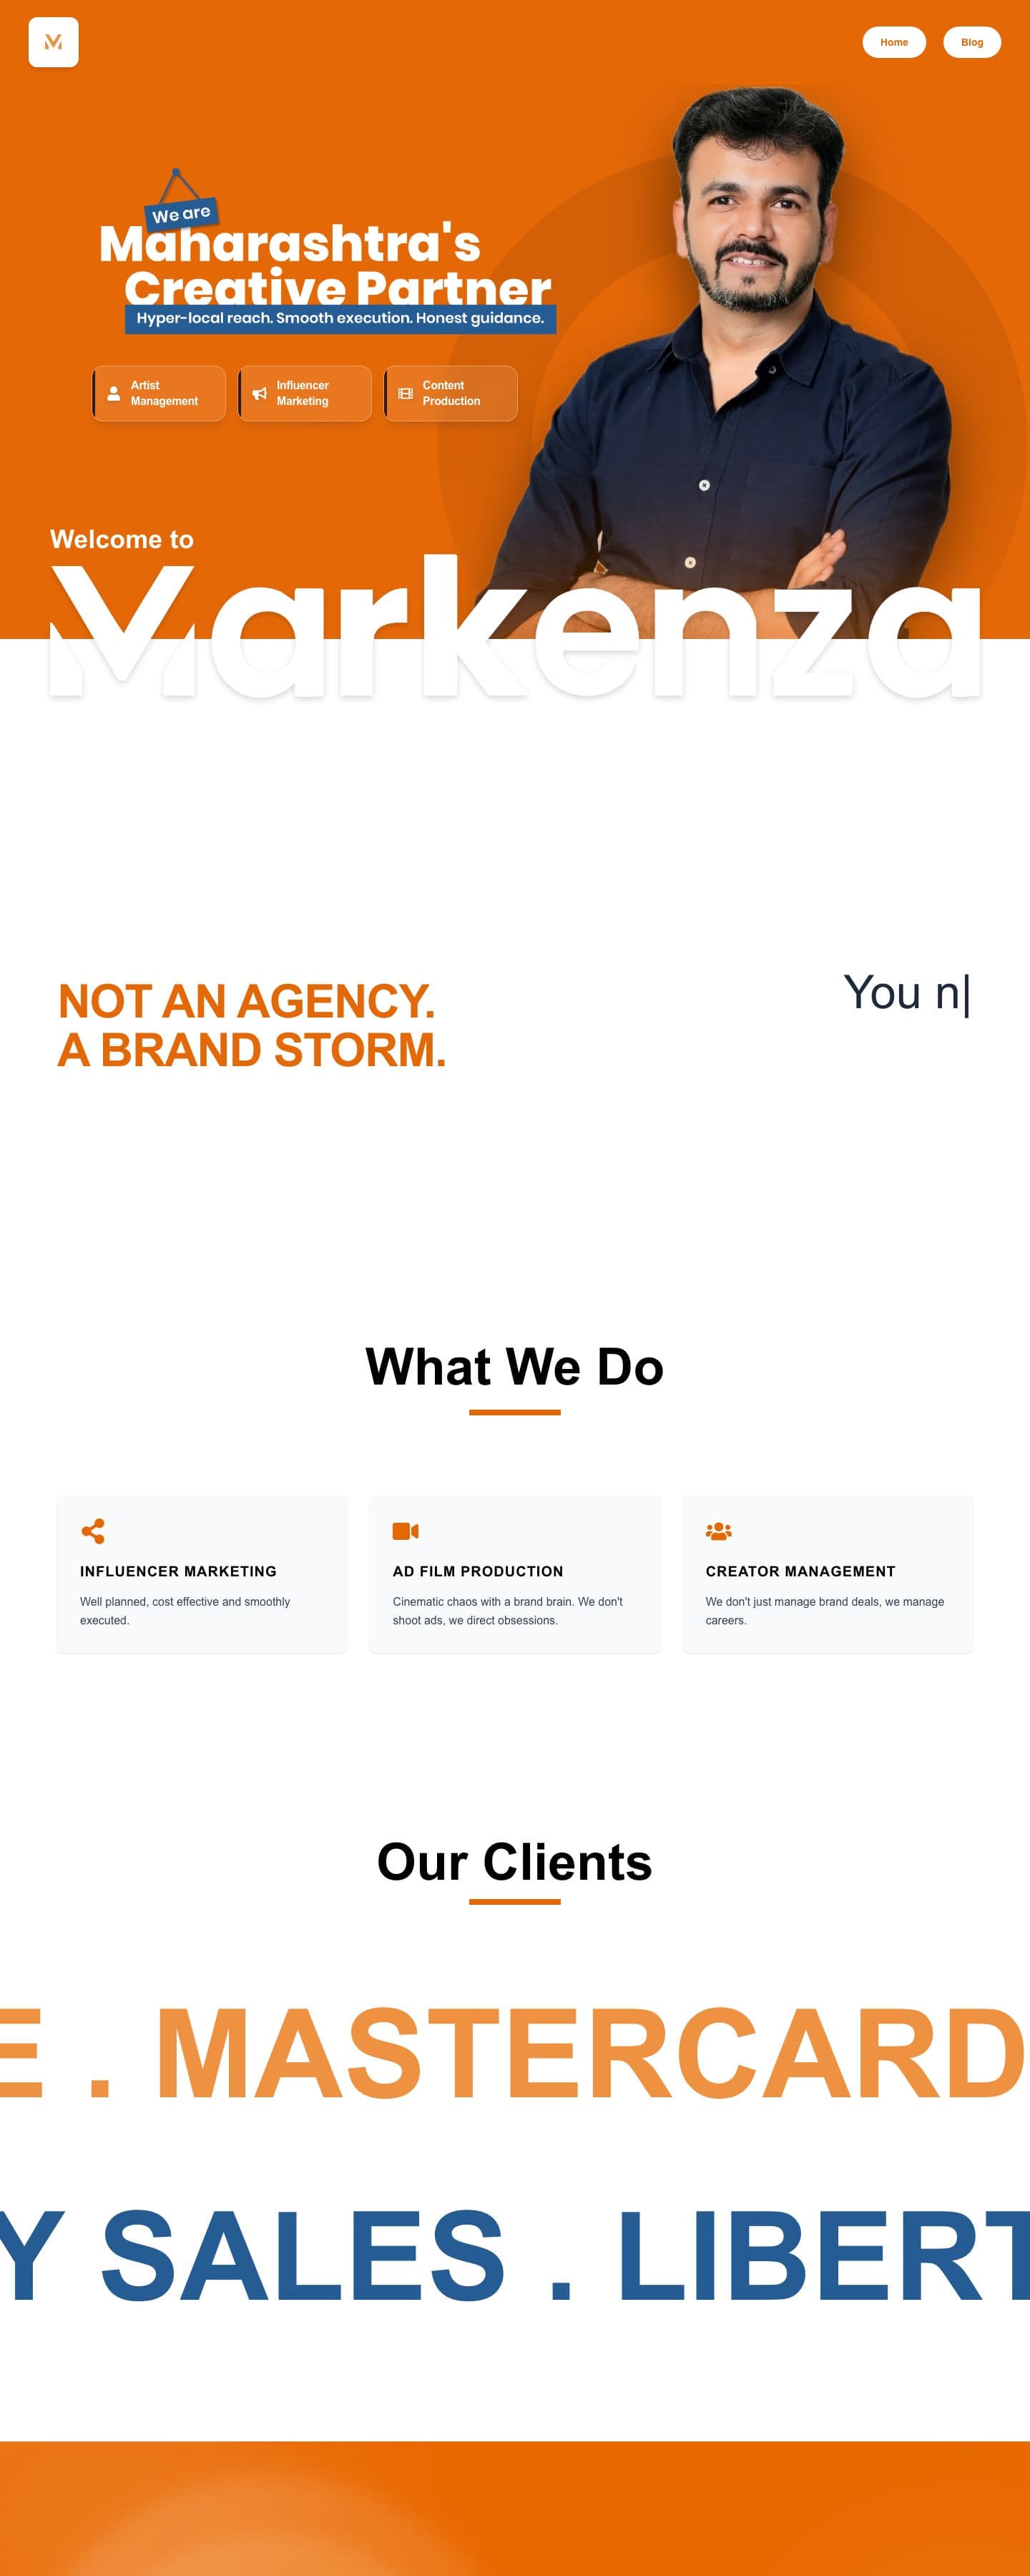
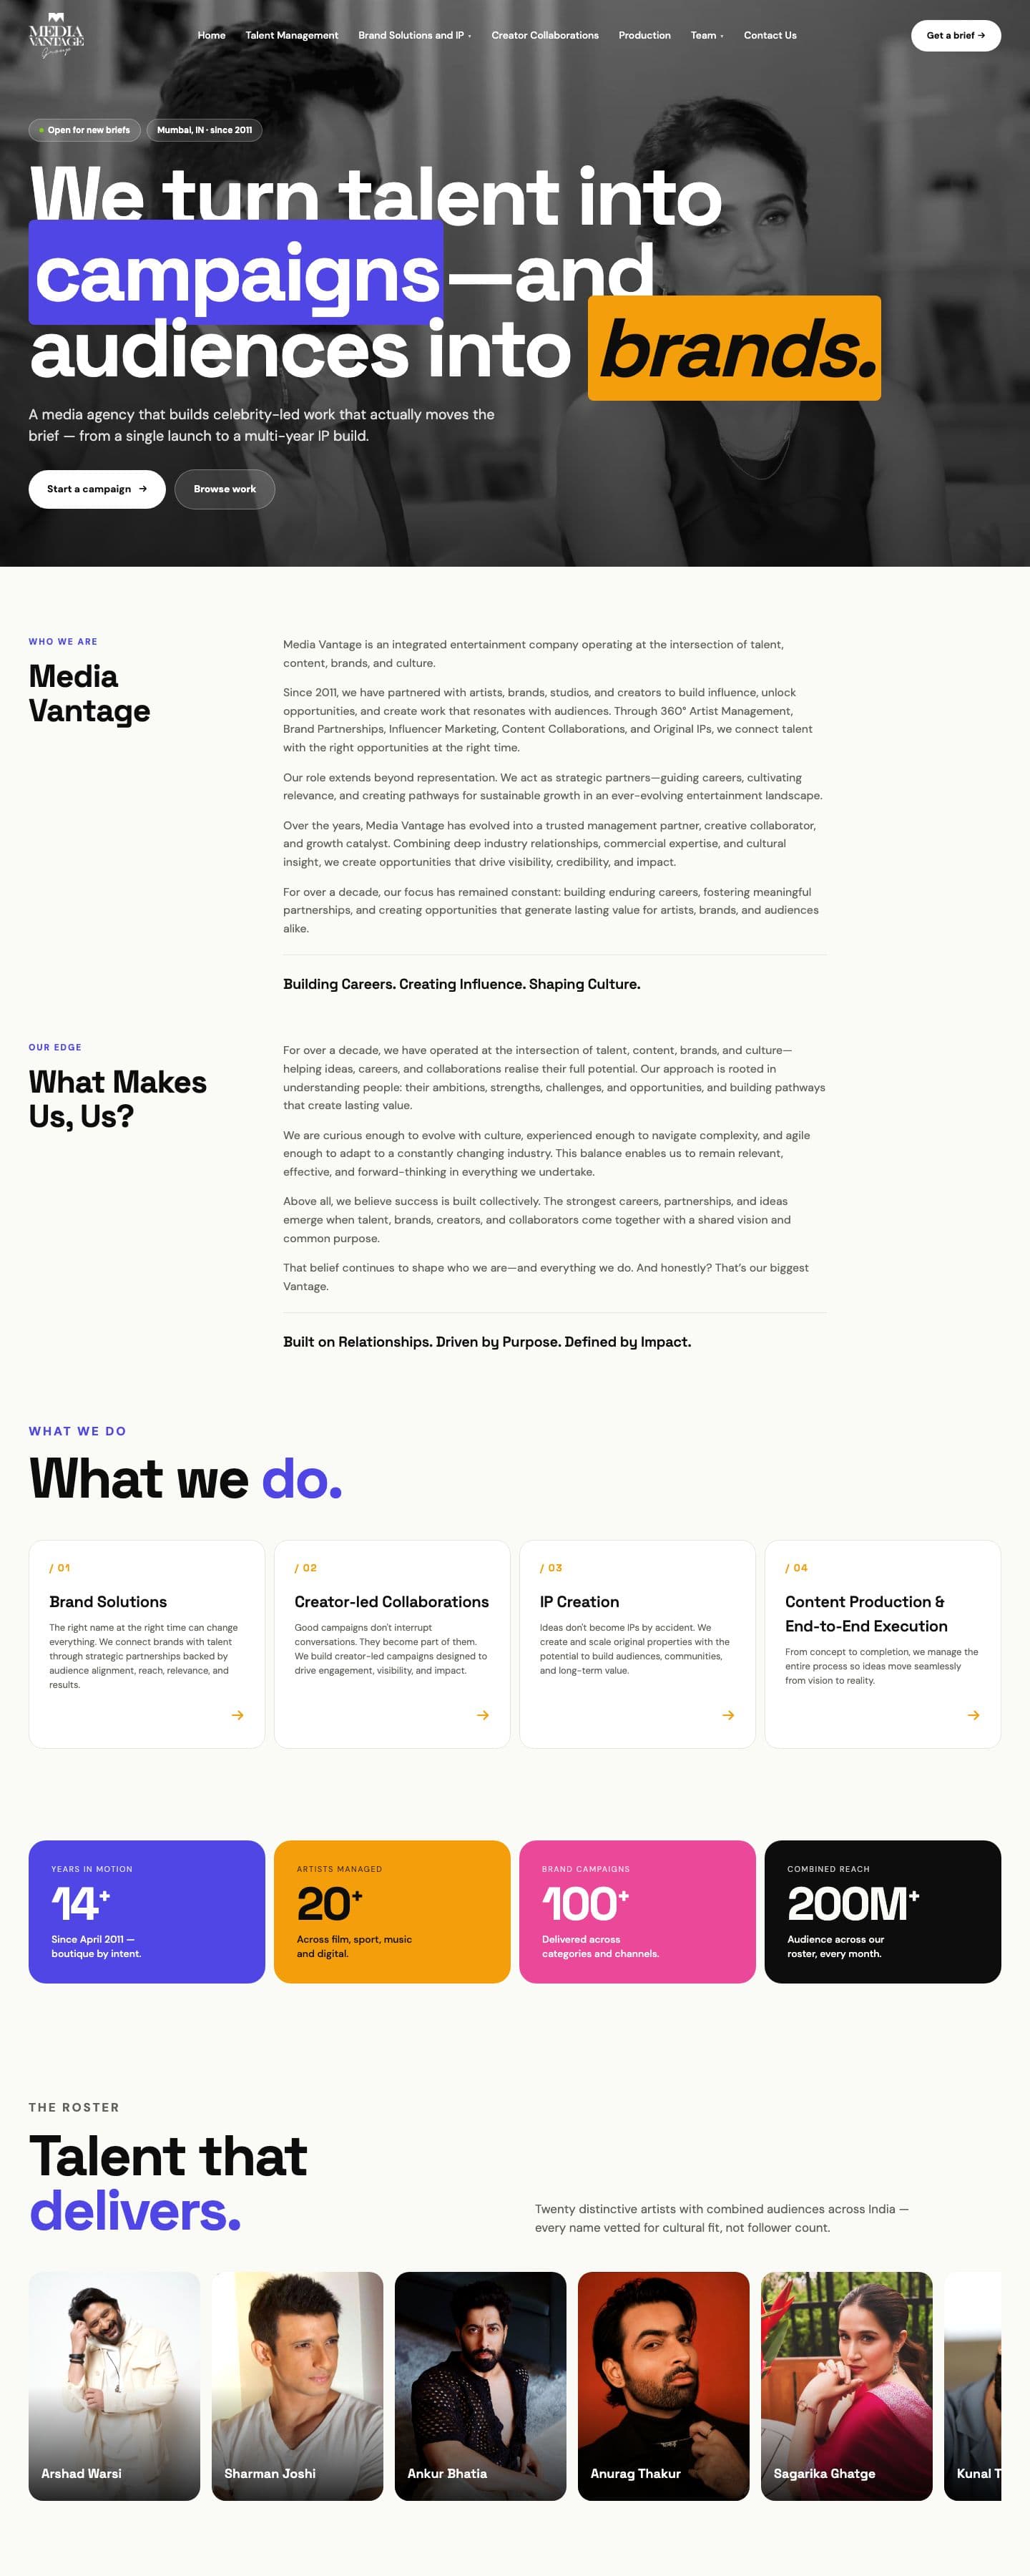
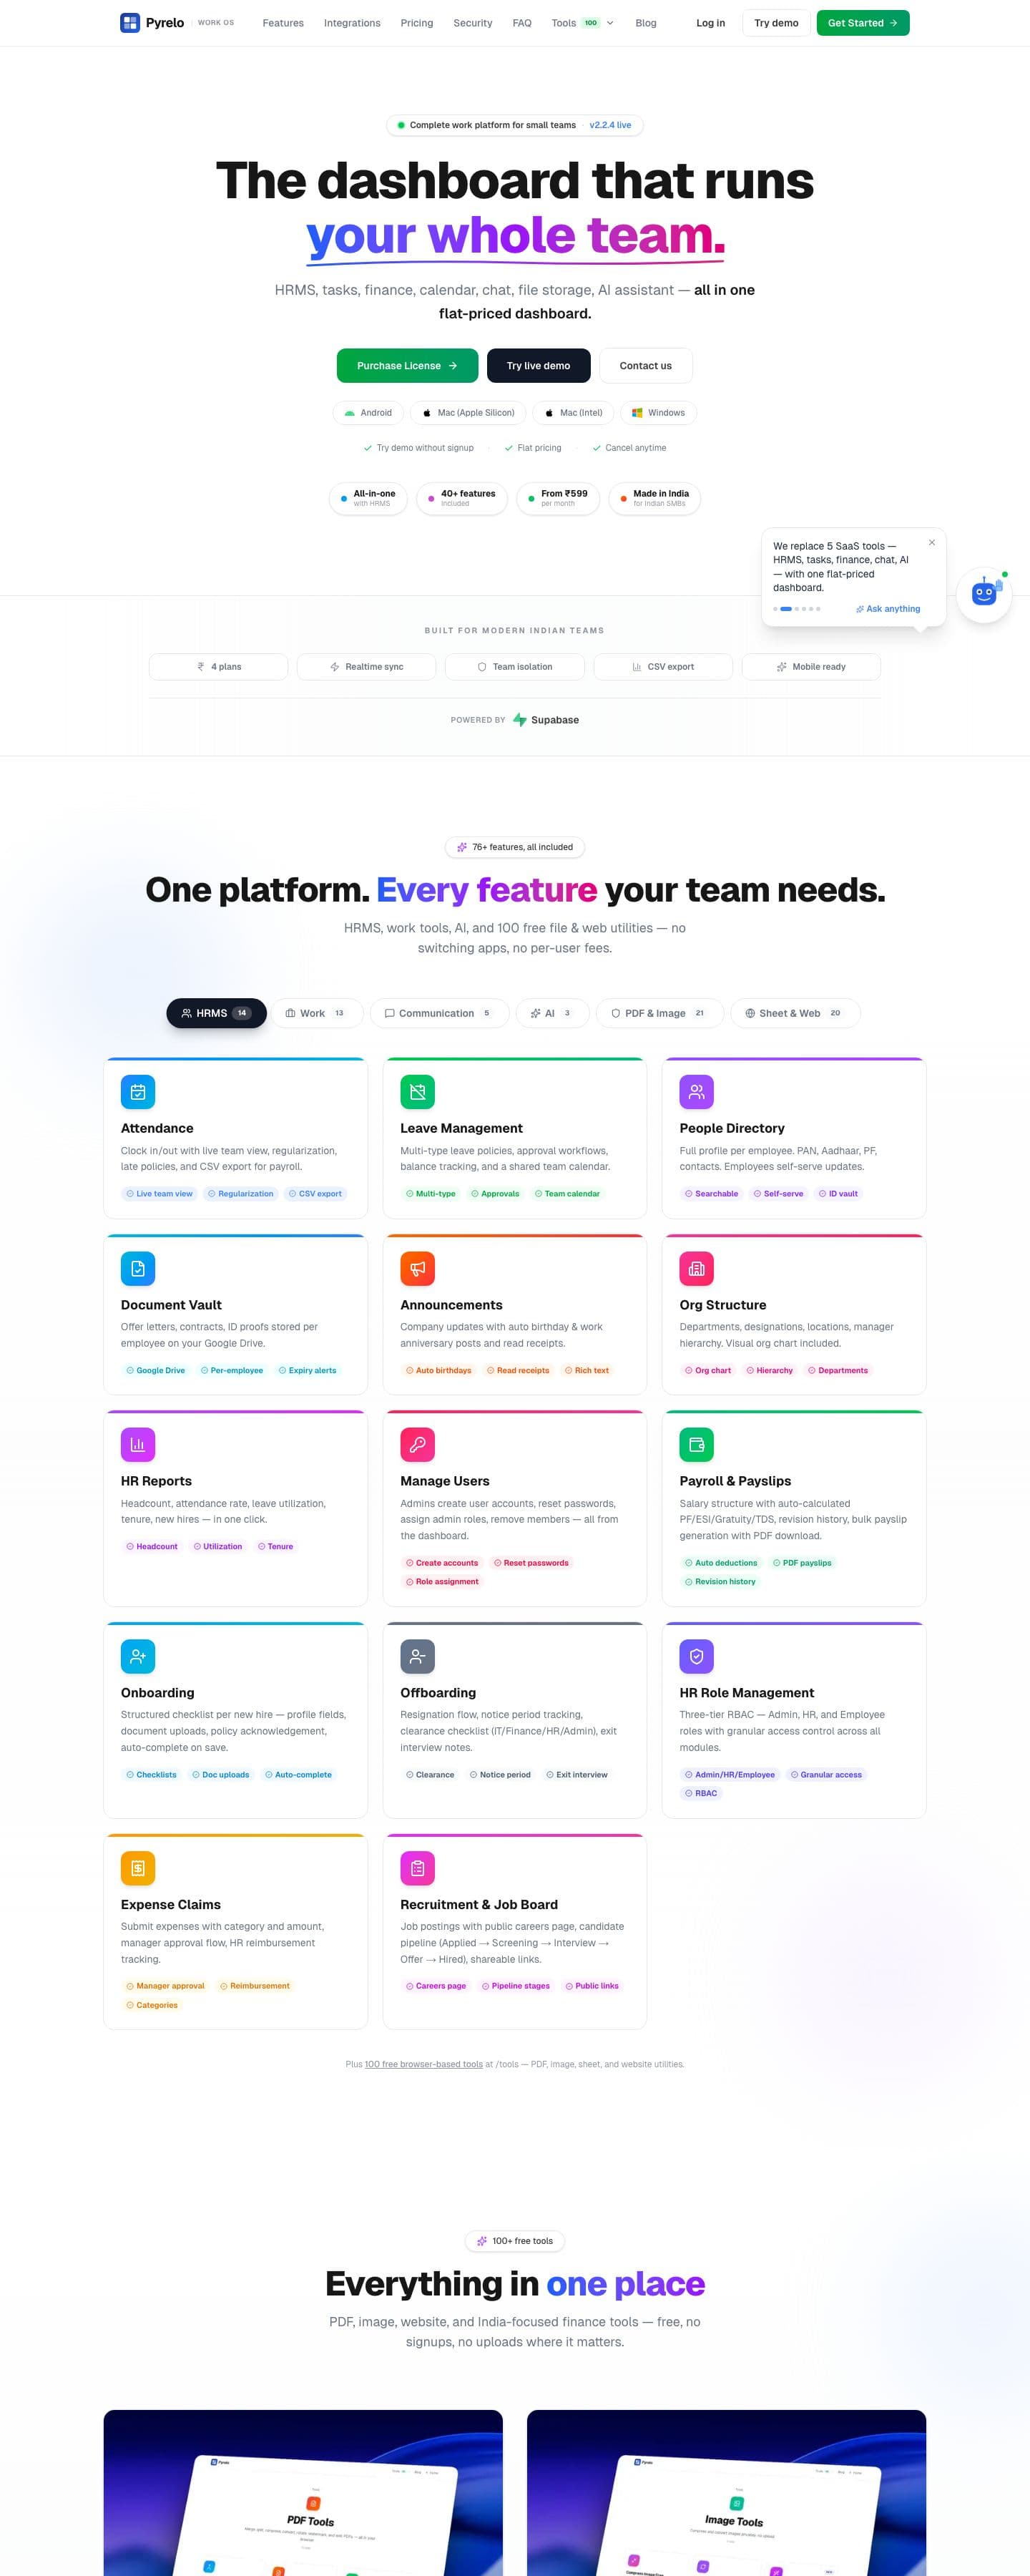
Five live websites, designed and built end to end, for a fintech, two agencies, a SaaS product and a fashion label.

eximpe.com
EximPe website
FeaturedFintech

EximPe

Cross-border payments that let global merchants collect UPI from Indian customers.

Moved the whole site from WordPress to Vite to Next.js, then wrote the SEO content, tools and lead forms that took it from 15 visitors a day to about 2,000.

100×
organic traffic
19.8k
URLs in sitemap
500+
qualified leads
  • Next.js
  • SEO
  • Lead capture
  • Automation
Visit eximpe.com

  1. 01

    Discover

    A call to understand the business, the audience and what success looks like.

  2. 02

    Design

    Wireframes, then a polished design you can click through before any code.

  3. 03

    Build

    Fast, accessible, SEO-ready code, shared on a live preview link as it grows.

  4. 04

    Launch and grow

    Hosting, analytics and search set up, then improvements based on real numbers.

Something else on your mind?

Jul 2026 to now, 162 releases

EximPe Compliance Toolkit

A self-hosted GRC and work-management platform that replaced Sprinto and ClickUp.

The console EximPe runs its ISO 27001:2022 programme on. Employees accept policies, finish security training and request access or hardware. Compliance managers run frameworks, controls, evidence, access reviews, drills and the regulatory calendar. Auditors get a read-only view that leads with what would fail. People can also file requests from Claude through its own MCP server.

Next.jsReactTypeScriptPostgreSQLPrismaTailwind CSSTerraformDockerGitHub ActionsClaude

Compliance program

ISO 27001:2022 controls

  • A.5.172-step verification is on for every accountfrom Google WorkspaceNot checked yet
  • A.8.24Every laptop has disk encryption onfrom JamfNot checked yet
  • A.8.8Macs run a macOS Apple still patchesfrom JamfNot checked yet
  • A.5.18Access is reviewed every quarterfrom Access reviewsNot checked yet
  • A.5.1Everyone accepted the security policyfrom PoliciesNot checked yet
Proven today0%

Interactive. Press the button to run the checks.

762
commits, 752 mine
162
production releases
121
database tables
152
API endpoints
466
test files
165k
lines of TypeScript

How it fits together

Follow the blue dot: one request on its way through the system.

People

Employees

requests, policies, training

Compliance team

controls, reviews, evidence

Claude

MCP with personal API keys

Next.js 16 app

Auth gate

Cognito sessions, MFA wall

Service layer

one rule set per domain

RBAC engine

capabilities and resource grants

Data and jobs

PostgreSQL

121 tables via Prisma

Nightly sweeps

checks, digests, integrity

S3, SES, Secrets Manager

files, email, credentials

Integrations

Google Workspace

MFA and account checks

Jamf

FileVault, macOS, check-ins

Sophos

device coverage, alerts

What it does

  • Access requests

    Multi-stage approval chains, permalinks, evidence with due dates, risk ratings.

  • Custom request types

    Owner-built forms and approval chains on one request engine.

  • Policy document control

    Parallel reviewers and an approver, signed in turn, with version history.

  • Acknowledgements

    Re-attestation cycles with append-only acceptance history.

  • Frameworks and controls

    ISO 27001:2022, 100 requirements, Statement of Applicability, evidence review.

  • Automated checks

    Nightly tests against Google Workspace, Jamf and Sophos, adopted per control.

  • Access reviews

    Quarterly recertification: keep, revoke, reduce or except, signed off as evidence.

  • Audit view

    Leads with defect counts, treats unknown as its own severity, minimises personal data.

  • Asset register

    Lifecycle, Jamf sync, end-of-life risk assessments, QR stickers.

  • Exercises and CAPA

    Tabletops and DR drills, corrective actions, approver-decided risk acceptance.

  • Compliance schedule

    Regulatory calendar with reminder ladders, participants and findings.

  • Training and campaigns

    Versioned modules with quizzes; one email per campaign, not per item.

Engineering decisions

One service per domain

Every authorization rule lives in a single service file. The web routes and the AI tools are thin adapters over it, so Claude cannot bypass a rule the UI enforces.

AI integration that cannot do harm

Seven read tools and one create tool, no approve tool. User-written text reaches the model marked as untrusted, and API keys are HMAC-hashed with a dedicated pepper.

One security wall, fail-closed

MFA and password-expiry enforcement lives in one module that every page, API and admin route passes through. A test lists every file allowed to bypass it.

History is append-only

Accepting v3 of a policy adds a row instead of overwriting v2, so the proof an auditor needs is never erased.

Status is derived, never stored

Control status and whose turn it is in an approval chain are computed on read, from one pure function shared by the page, the inbox and the nightly chase.

Guard tests as architecture

Source-scanning tests pin route guards, PII minimisation, safe secret deletion, CSV-injection safety and email escaping.

Most of my work lives in private company repositories. These are the totals.

2,640
GitHub contributions since January 2025
1,577
commits in the last twelve months

Every day, October 2025 to October 2026

Busiest day, ringed in blue: 98 commits on 23 Sept 2026.LessMore

Commits counted from EximPe repositories, October 2025 to October 2026. Contribution totals are from my GitHub profile with private work included: 1,034 in 2025 and 1,606 in 2026 so far.

Where the commits went

  • eximpe.com

    909 commits since Apr 2025

    The company website: Next.js, Supabase, Ghost CMS, 126 pages, five free tools, Chinese, Japanese and Korean editions.

  • Compliance Toolkit

    836 commits since Jul 2026

    ISO 27001 console that replaced Sprinto and ClickUp.

  • DLP

    231 commits since Jul 2026

    Swift agent, Chrome extension and admin console.

  • Production infrastructure

    28 commits since Aug 2026

    Terraform for the toolkit's isolated AWS account.

  • Team Claude skills

    10 commits since Sep 2026

    Skills that file compliance requests from a chat.

3+ years full-time across product, web, growth and security, plus freelance client work.

  1. Jul 2024 to now2 yrs 4 mos

    EximPe

    Product Development & Marketing

    Bangalore, full-time

    An RBI-licensed cross-border payments company. I own the website and its growth, run audit readiness for PCI DSS, RBI and ISO 27001 (including the internal ISO audits), designed and built the company's internal compliance and security products, and run its IT.

    100×
    organic traffic
    500+
    qualified leads
    2,640
    GitHub contributions
    162
    toolkit releases

    Website and growth

    • Led the complete migration of eximpe.com from WordPress to Vite to Next.js on my own, end to end, keeping search rankings with about 260 managed redirects.
    • Designed and built both the frontend and the backend, for a smooth experience and an architecture that stays easy to maintain.
    • Grew daily organic traffic from 10 to 15 visitors to about 2,000 with SEO-led content, comparison pages and four language editions.
    • Built six free trade tools, including an HSN finder with about 19,000 programmatic pages generated from government tariff data.
    • Built the lead pipeline behind 500+ qualified leads: validated forms, AES-256-GCM field encryption, sales alerts and a one-click follow-up.
    • Made the site readable by AI answer engines with llms.txt, structured data on about 39 page types and a grounded Ask AI feature.

    Compliance and security products

    • Designed and built the EximPe Compliance Toolkit, which replaced Sprinto and ClickUp and runs the company's ISO 27001:2022 programme: 121 tables, 152 API endpoints, 162 production releases.
    • Built EximPe DLP: a Swift macOS agent, a Chrome extension and an SMTP gateway sharing one detection engine with real checksums.
    • Wrote the MCP server and Claude skills that let anyone at EximPe file a compliance request from a chat, with no ability to approve one.
    • Set up the AWS infrastructure in Terraform: ECS Fargate, RDS, Cognito, S3 and SES, deployed from GitHub Actions with OIDC and no stored keys.

    Audits and regulatory compliance

    • Run audit readiness for PCI DSS v4.0.1 as a payment service provider, the RBI-mandated annual system and cyber security audit by CERT-In empanelled auditors, and ISO 27001:2022.
    • Conduct EximPe's internal ISO 27001 audits myself, covering clauses 4 to 10 and the Annex A controls, and report the findings to management.
    • Prepare the evidence and work alongside the assessors: quarterly ASV scans, VAPT, access reviews, policy reviews, DR drills and incident-response tests.
    • Track EximPe's RBI Payment Aggregator (PA-CB) obligations, from quarterly InCA and OCA bank certificates to monthly cyber incident reports, in a compliance calendar I built.
    • Close audit findings through corrective actions backed by proof, with every accepted risk approved by a named approver and given an end date.

    IT and operations

    • Run the company's Mac fleet on Jamf: enrolment, configuration profiles, FileVault, patching and self-healing agents.
    • Manage endpoint security on Sophos and Google Workspace administration, including quarterly access reviews.

    Marketing and automation

    • Planned, designed and ran Google and Meta ad campaigns on controlled budgets, with ad creatives built in After Effects.
    • Automated weekly news publishing with Relay.app, Make.com and Ghost CMS: an RSS trigger publishes every Tuesday with no manual work.
    • Automated lead workflows with webhooks, homepage forms and email sequences, so every lead arrives CRM-ready.
    • Ran design audits, content creation and marketing optimisation, keeping product, brand and growth aligned.
    Next.jsTypeScriptPostgreSQLPrismaSupabaseSwiftTerraformDockerGitHub ActionsGoogle AdsMetaClaude
  2. Alongside full-time work5 live sites

    Freelance

    Web designer and developer

    Remote

    Websites for agencies, a SaaS product and a fashion label, designed and built end to end.

    Selected clients

    • Markenza, a Marathi influencer marketing agency: designed and built the full company site, a performance-optimised, SEO-ready platform, plus the blog backend the team publishes from.
    • Media Vantage, a Mumbai entertainment company: a type-led site for celebrity campaigns and brand IP.
    • Pyrelo, a work dashboard for Indian teams: product site, pricing, demo flow and a library of free tools.
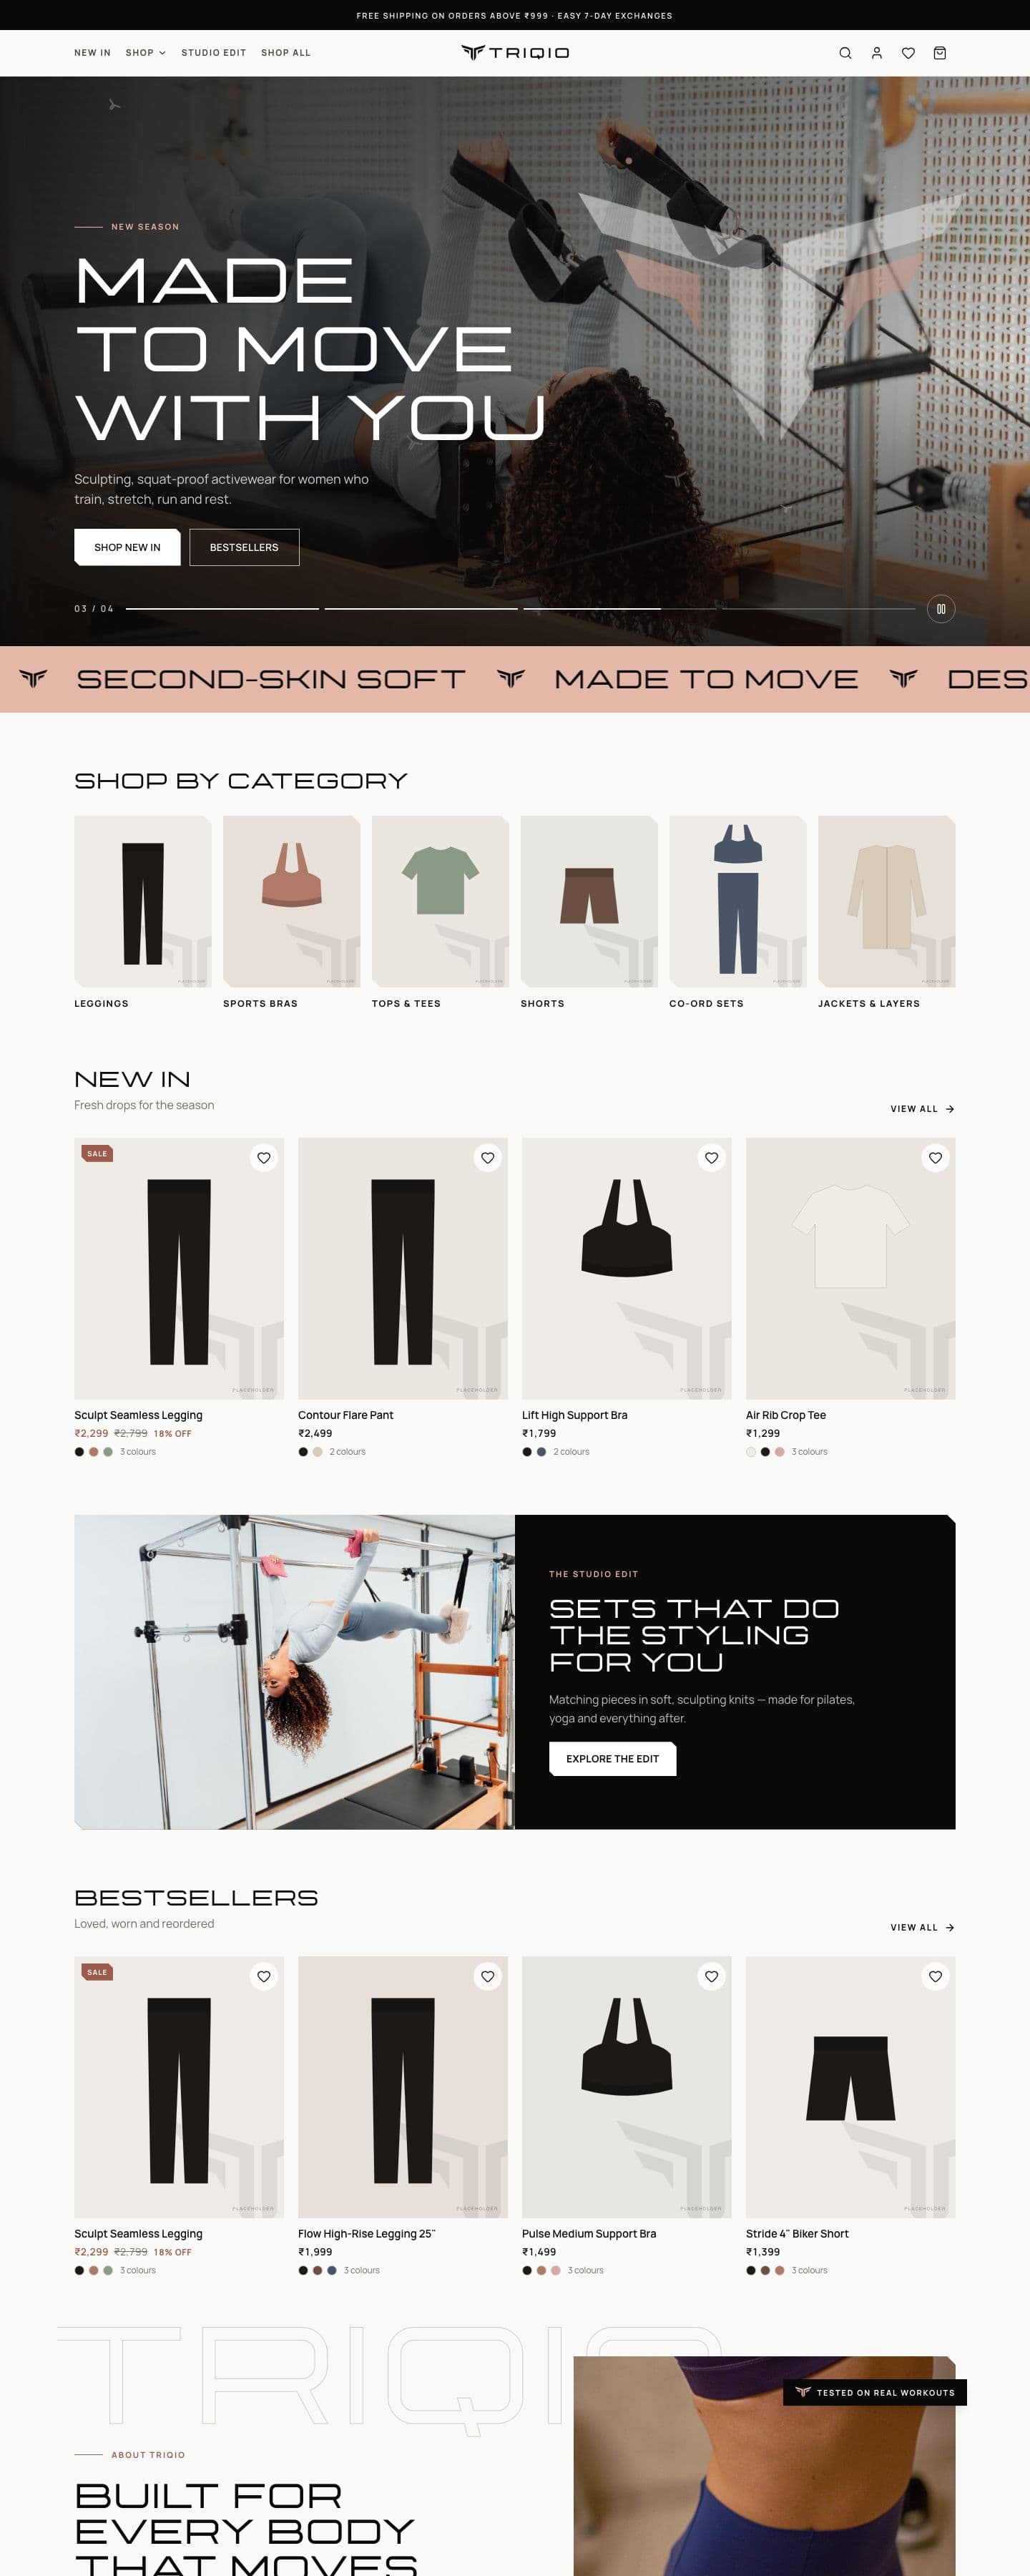
    • Triqio, an activewear label: e-commerce storefront with collections, product pages and a studio edit.
    Next.jsReactTailwind CSSFigmaVercel
  3. Jan to Jul 20247 mos

    Alme App

    Full Stack Developer

    Bangalore

    Full-stack work across the product's web properties.

    What I did

    • Built and maintained features across Laravel, PHP, WordPress and Next.js.
    • Worked on backend logic, CMS customisation and frontend performance optimisation.
    • Collaborated with cross-functional teams to ship production-ready features on deadline.
    LaravelWordPressNext.js
  4. Jan to Aug 20238 mos

    Shubhchintak Technology

    Frontend Developer

    Remote

    Frontend work on a React application.

    What I did

    • Built responsive user interfaces with React and Tailwind CSS.
    • Translated UI and UX designs into high-quality, reusable frontend components.
    • Improved the app's performance and consistency across devices.
    ReactTailwind CSS
  5. B.Tech, Computer Science & Engineering

    Graduated 2023

How I work

Ownership across domains

One person across tech, marketing and IT, so nothing falls between teams.

Concept to launch

I lead projects on my own, from the first sketch to the live site, including end-to-end migrations.

Fast with AI

AI tools are part of how I build, write and automate, which is how one person ships this much.

Capabilities

Build

  • Next.js
  • React
  • TypeScript
  • JavaScript, HTML5, CSS3
  • Vite
  • Tailwind CSS
  • PostgreSQL & Prisma
  • Supabase
  • Laravel & PHP
  • WordPress & Ghost
  • Swift (macOS agents)
  • Chrome extensions
  • MCP servers
  • Claude skills

Ship

  • AWS ECS Fargate
  • Terraform
  • Docker
  • GitHub Actions
  • Cognito
  • Secrets Manager
  • SES

Grow

  • SEO & content
  • Google Ads
  • Meta Ads
  • Conversion tracking
  • Make.com
  • Relay.app
  • Webhooks & RSS automation
  • After Effects creatives
  • Design audits
  • AI-assisted content

Secure

  • PCI DSS v4.0.1
  • RBI PA and PA-CB compliance
  • CERT-In requirements
  • ISO 27001
  • Jamf MDM
  • Sophos Endpoint
  • Google Workspace admin
  • Access reviews
  • ISO 27001 internal audits
  • VAPT and ASV coordination
  • Audit evidence and CAPA
  • Data loss prevention

Mostly cats, if I'm honest. Also biryani, long drives, night rides and go-karting.

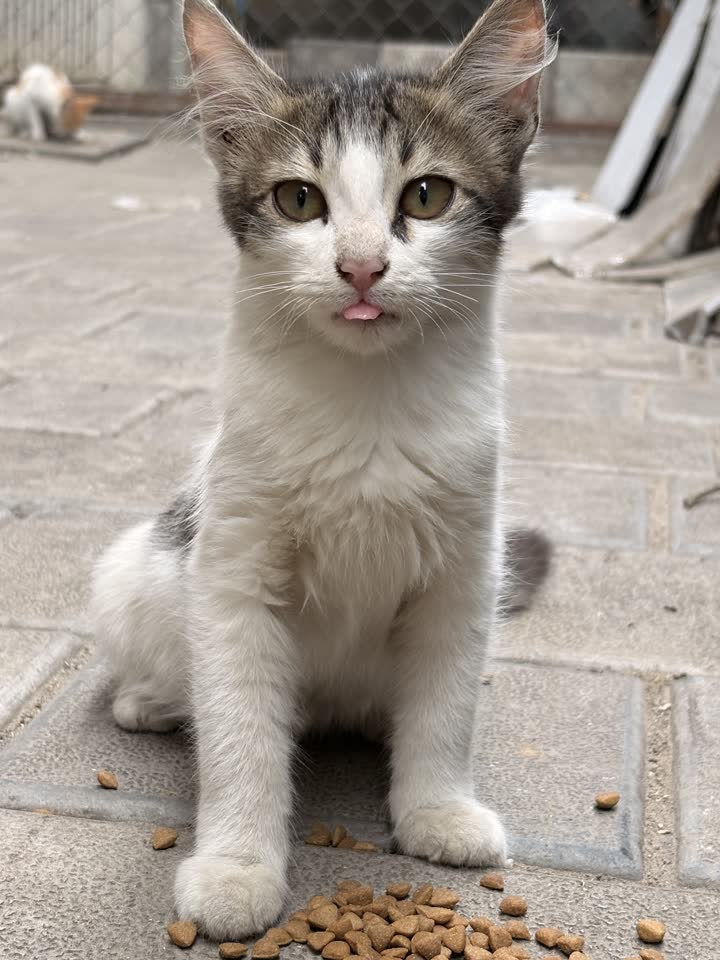
  • Feeding the street cats

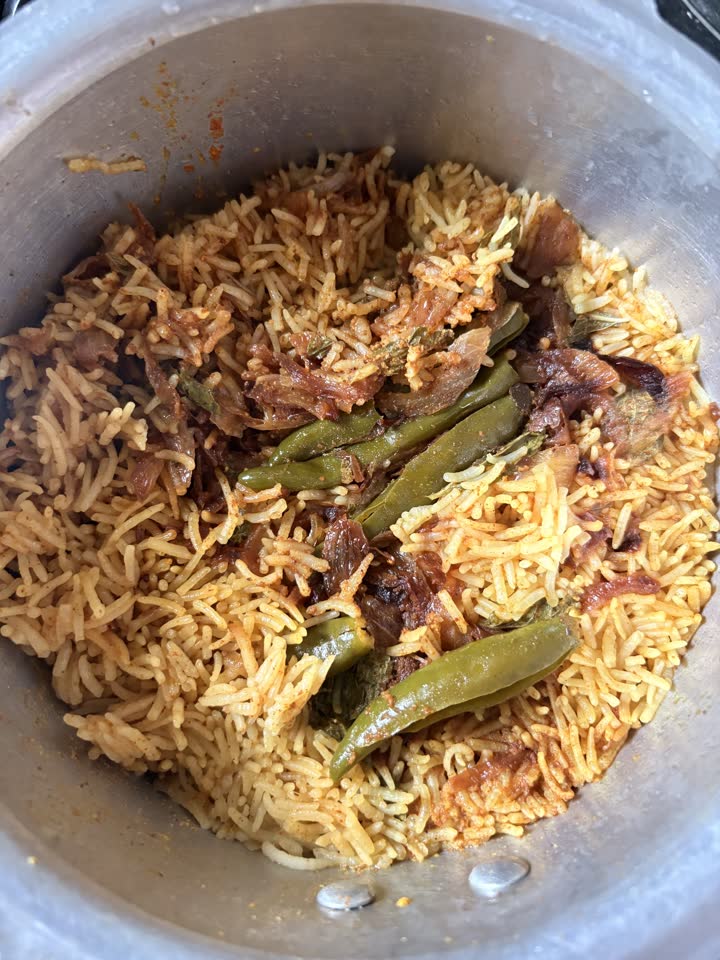
  • A pot of biryani I cooked

    Biryani, cooked by me

  • I love a long drive

  • A kitten sticking its tongue out

    Blep.

  • Night rides with the gang

  • Go-karting, full throttle

  • Paid in head scratches

  • Clearly, I like cats.

    So the whole site has a cat mode.